DORA stands for Digital Operational Resilience Act. This European regulation (EU) 2022/2554 has applied since 17 January 2025. DORA ensures that financial institutions can withstand ICT disruptions and cyber attacks, and recover from them quickly.
DORA applies to more than twenty types of financial institutions, such as banks, insurers, pension funds, investment firms and payment institutions. In the Netherlands, DNB and the AFM supervise compliance. The management body carries final responsibility, and all staff must complete awareness and training.
Measure:
Set up a framework to identify ICT risks, protect your systems, detect anomalies and recover quickly. The management body approves this framework and carries final responsibility for it.
Measure:
Make sure board members have sufficient knowledge and skills to understand and assess ICT risks. DORA requires them to follow specific training on a regular basis.
Measure:
Include security awareness and digital operational resilience training as a compulsory part of your training programme, for all staff and senior management. For example with Arda's cyber security awareness e-learning.
Measure:
Establish a process to detect, classify and handle ICT incidents. Major ICT incidents must be reported to the supervisor, such as DNB or the AFM.
Measure:
Test your systems and processes regularly under a testing programme. Institutions designated for it also carry out a threat-led penetration test (TLPT) every three years.
Measure:
Keep a register of your ICT providers and make clear contractual arrangements. Where appropriate, include ICT service providers in your awareness training.
DORA sets clear requirements for the knowledge and behaviour of staff and management. The Arda platform helps you meet those requirements in a structured way.
Article 13(6)
Arda combines e-learning, interactive films, serious games and phishing training in one platform. That makes awareness a permanent part of your training programme.
Matched to the role
DORA asks for training that fits the employee's role. With learning paths you decide which modules each group receives, in what order and at what pace.
Demonstrable
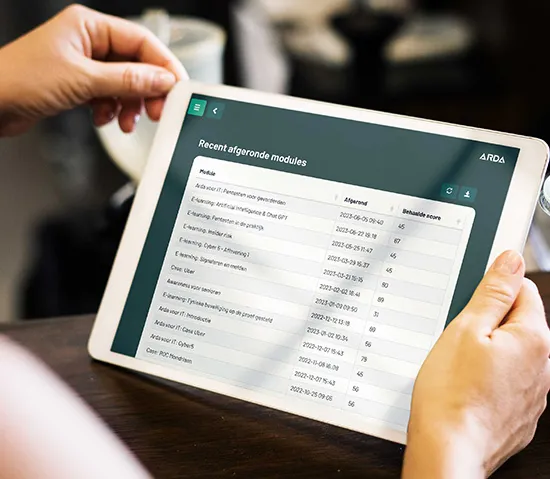
You see exactly who has completed which components. That lets you show what your organisation does during an audit or a request from the supervisor.
ICT third parties
Arda is itself an ICT service provider in your chain. Arda is ISO 27001 certified, so you can account for this provider properly too.
Do you want to demonstrably meet DORA's awareness requirements? Arda helps staff and management recognise digital risks and respond to them properly.
Yes. Article 13(6) of DORA requires financial institutions to include ICT security awareness programmes and digital operational resilience training as a compulsory part of their staff training. This applies to all employees and to senior management.
Yes. Under Article 5, members of the management body must have sufficient knowledge and skills to understand and assess ICT risks and their impact. Among other things, they do this by following specific training on a regular basis.
NIS2 is a broad European directive on cyber security in essential and important sectors. DORA was made specifically for the financial sector and takes precedence over the general NIS2 rules for financial institutions.
Aware employees who know how to keep cybercriminals out.
50% more reports of suspicious emails by employees.
Less stress about reputational damage and recovery costs after an incident.